
What is DELOL Sovereign Digital Signature Private CA Infrastructure?
The DELOL Sovereign Digital Signature Private CA Infrastructure is an upgrade from DELOL Sovereign Self-Signed Certificates.
While the DELOL Sovereign Self-Signed Certificates were intended for enhancing the standard self Signed Certificates with DELOL Shield’s 256 Byte Factorial Entropy as Digital Notary Seal, which hardened those self-signed certificates to render them tamper-proof from cybersecurity perspective.
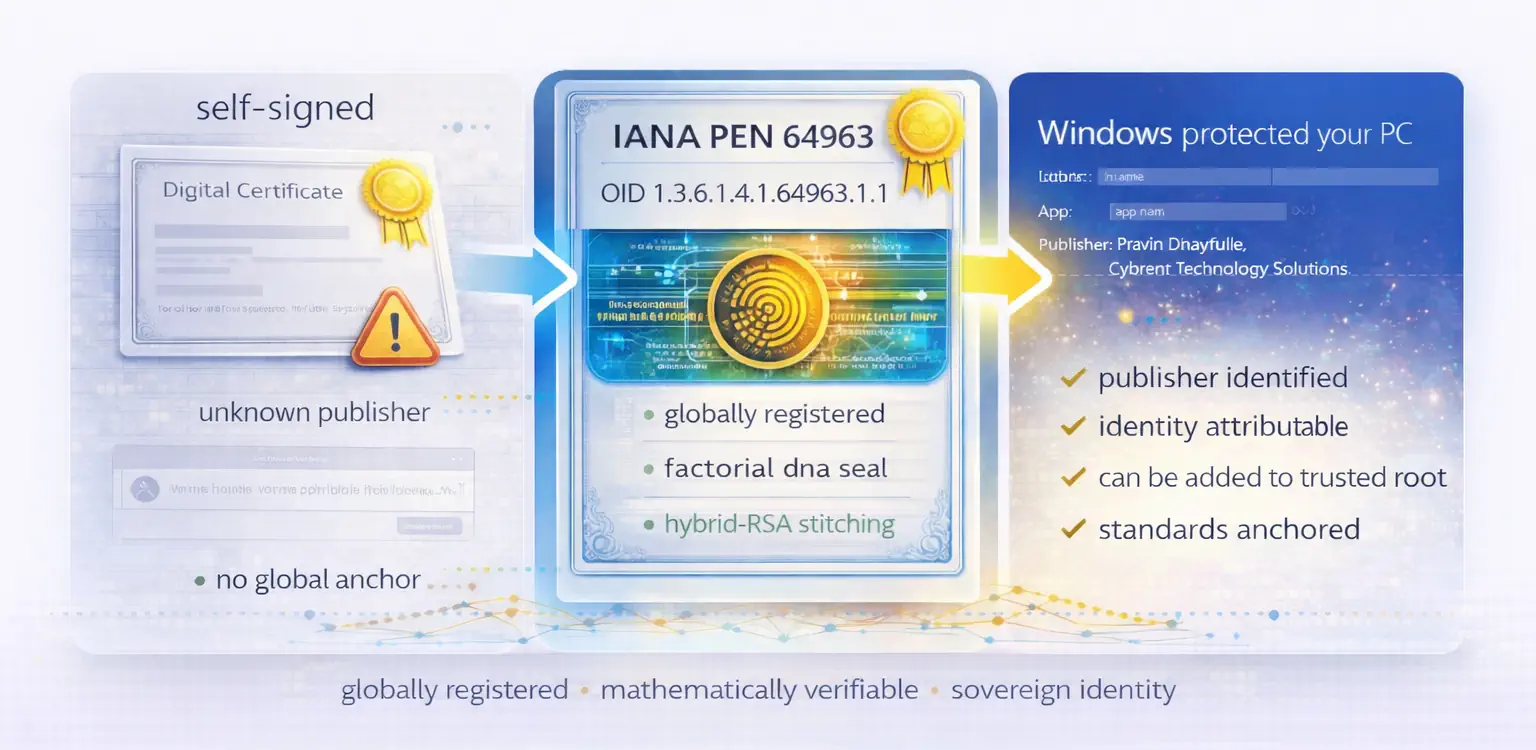
Figure 1: DELOL Sovereign Self-Signed Certificates Functional Structure
This illustration which you see above explains how the Factorial Entropy Seal is tagged to the official IANA PEN 64963 allocated to Cybrent Technology Solutions through auditable and traceable OID Hierarchy. Being a hybrid certificate, it is compatible with OpenSSL and Microsoft Signtool.
The OID acts as a security layer which governs the authenticity and strength of the certificate as the attackers cannot recreate this Digital Seal when they try to “forge” a Clone of this certificate.
The blue screen of Windows Defender’s executable file alert shows the Publisher and the Organisation of the Certificate owner.
Since this experiment of hardening standard Digital Certificates with DELOL Entropy became successful, Pravin Dhayfule – The CEO of Cybrent Technology Solutions, decided to build a private Sovereign CA Infrastructure as a private secured digital signature certification infrastructure for the enterprises such that those enterprises can establish a hierarchy of highly secured Certificates to be used within the organisation which has traceability, auditability and a strenghth against misuse and forgery as compared to standard self-signed certificates.
What is the architecture of DELOL Sovereign Digital Signature Private CA?
DELOL Sovereign Digital Signature Private CA follows the standard architecture and hierarchy established by the industry
This illustration explains the hierarchy and purpose of the DELOL Sovereign Digital Signature Private Certificate Nodes.

Figure 2: DELOL Sovereign Digital Signature Private Certificate Hierarchy
The Root CA is the primary Organisational Identity Authority which is used for signing the Intermediate Issuer CA which is used for issuing Individual Digital Certificates that are used for signing documents and code.
This is the same hierarchy followed by the standard commercial public Certificate Authority.
The only difference is that this entire architecture is offline CLI driven such that the keys and the certificate generation are completely private affair and can never be sniffed through Trojans and Botnets, thus adding an extra level of security by design to safeguard these organisational digital identity artefacts.
The Benefit of this Hierarchy
- The Root CA and it’s keys always remain isolated such that only the CRT file is accessible for hierarchy audit whereas the keys are always hidden and locked using the DELOL Shield platform safeguarded away from access of unauthorized users.
- The Intermediate Issuer CA is inherited from the Root CA and is used for issuing the Child Certificates to be assigned to the individuals.
- Since this is a private enterprise CA infrastructure the department heads will be assigned Department Specific Intermediate CAs for their departments with they being accountable for safeguarding the keys to avoid them from being misused by unauthorized users.
- The department heads will be the authorities to issue the individual certificates to their employees
- A Centralized Portal can be established for broadcasting the hierarchy of the issued and revoked certificates so that systems are aware of authentic and genuine certificates.
Example of the Hierarchy
L1 – Root CA:
Signing Certificate Chain:
Issued to: DELOL Sovereign Root CA
Issued by: DELOL Sovereign Root CA
Expires: Fri Aug 31 18:36:28 2046
SHA1 hash: 26995A137AC2D6D9263B9CCA2834457D899889F9
L2 – Intermediate Issuer CA:
Issued to: DELOL Sovereign Intermediate Issuing CA
Issued by: DELOL Sovereign Root CA
Expires: Wed Sep 03 13:38:06 2036
SHA1 hash: B5B30DB8C4299961698B9B8A824BB31EE4B8C8E1
L3 – Individual Certificate:
Issued to: Pravin Dhayfule
Issued by: DELOL Sovereign Intermediate Issuing CA
Expires: Fri Sep 05 13:41:33 2031
SHA1 hash: 82B9AF07D7EBF4B0317352EBEF4FD9E5DC8ED915
How are DELOL Sovereign Digital Certificates immune to Forgery?
The Offline Mode of Operations
As we already saw that the certificates are not generated over the web or cloud infrastructure, which makes the entire Certificate Generation Architecure a complete blindspot for sniffers, trojans and botnets who try to break into the infrastructure to steal the keys.
Hybrid Stitched Architecture
Being a cutom layered and tailored hybrid Digital Certificate these certificates can never be generated with the standard tools available in market such as OpenSSL or Signtool.
The certificates are individually generated through three independent offlline CLI Utilities:
- The Root CA Generator: This is the one time utility that generates the Root CA Certificate with a validity of 20 years, the Private Certificate Key and the DELOL Entropy Seed. This utility is only kept with the authority at the higher level who will govern the Root CA.
- The Intermediate Certificate Generator: This is another independent utility that asks the user to provide the Root CRT file, the Private Certificate Key of the Root CRT and the DELOL Entropy Seed of the Private CA based on which the Intermediate CA Certificate is generated along with it’s Private Certificate Key and it’s DELOL Entropy Seed. This utility is only kept with the Department level authority who will govern the Intermediate CA of their respective department.
- The Individual Certificate Generator: This is the third and again independent utility that asks the user to provide the Intermediate CA CRT file, it’s Private Certificate Key and it’s DELOL Entropy Seed based on which this individual certificate is generated. This utility again is only kept with the Department level authority who will govern the issuance of the code and document signing certificates to the members of their respective department.
All these utilities are independent and do not share any central or common dynamic linked library, which again defeats the attackers by preventing them from sniffing the common functions. And so these utilities can be isolated department and owner wise.
Finally the most crucial – DELOL Sovereign Certificate Verifier
This is a verification utility that asks users to provide the CRT file of which it performs a deep-tissue DNA analysis to identiy the DELOL Enrtropy Seal embedded within the Certificate.
The snapshot:
Enter Certificate Filename or Full Path (e.g., identity.crt): Pravin_Dhayfule_DELOL.crt
[Sovereign Identity Detected]
——————————
Subject Name: CN=Pravin Dhayfule, O=Cybrent Technology Solutions
Email: 0�pravin@dhayfule.com
Issuer: O=Cybrent Technology Solutions (OPC) Pvt. Ltd., CN=DELOL Sovereign Intermediate Issuing CA
Serial Number: 00b12531f5ddfdfb1873a3fb35ac69831c
Validity: 2026-09-06T08:11:33Z to 2031-09-05T08:11:33Z
Public Key: RSA (2048-bit)
Subject Key ID: bdd473a88a84fa4bb44ac20a073b9cd0d7a2608dea10003259c7f97fa641ad89[Standard X.509 Purpose & Usage]
——————————
Key Usage: Digital Signature, Key Encipherment
Extended Usage: Code Signing, Client Authentication[DELOL Specific Architecture (Proprietary)]
——————————
Sovereign Purpose: Digital Asset End-Entity Certification
Sovereign Identity: Cybrent Technology Solutions (OPC) Pvt. Ltd.
Certification Suite: DELOL Sovereign Certification Suite
Attestation Type: DELOL Sovereign Seal
Sovereign Verification: Factorial Entropy Seal [DETECTED]
Factorial Entropy Seal (Hex): 6f00176f57e155f749c7bbac14328f24…
Generator Origin: PEN 64963 (Official IANA Arc)
Stitching Protocol: Hybrid-RSA / DELOL-3[SUCCESS]: SOVEREIGN LINEAGE DETECTED.
[INFO]: Standard Audit Complete. Sovereign validation successful
The benefit of this verification tool is to check if the certificate is really genuine or counterfeit forged certificate. Since the standard tools available in market do not have the DELOL Entropy Seed they wont be able to replicate the genuine Sovereign Lineage Seal and that would fail the test immediately. Even the smartest and capable Quantum AI won’t be able to reproduce the DELOL Entropy Seal because it’s a closed source secret.

Figure 3: Snapshot of the DELOL Sovereign Certificate Verification Tool
This is how the certificate appears in the Windows Certificate Viewer
The set oof screenshots below are from the same certificate of which we saw the hierarchy as well as the verification snapshot.
The three screenshots represent:
- The Certificate Path or the Hierarchy which we discussed earlier.
- The Issuer and other standard identity metadata of the certificate.
- These are the tailored extensions and the highlighted one is the actual DELOL Entropy Seal also called as the Sovereign Lineage mentioned in the Verification Tool.

Figure 4: How the DELOL Sovereign Certificate appears in the Windows Certificate Viewer
Is the DELOL Sovereign Digital Signature CA alternative to Public Trust CA?
The straightforward answer to this question of whether DELOL Sovereign Digital Signature Private CA Infrastructure is directly a replacement or alternative to the third-party commercial public trust CAs like Digicert, Comodo, eMudhra, Capricorn CA, etc. is a big “No”.
Reason being that those commercial Public Trust Certificates are licensed and authorized by the Government authorities for regulatory, government, taxation and other public document signing as they are subject to KYC of the individuals as per the government laws.
DELOL Sovereign Digital Signature CA Infrastructure has a completely different use case. This is meant to establish a standard internal and private digital signature infrastructure to establish trust and verification of digital assets that solely are governed by the organisation.
To understand it from perspective of real-life use case lets consider these scenarios.
Scenario 1 – Internal attestation of crucial and confidential documents to deter forgery and malpractice
Imagine that your organisation is into audit, defence, security or into a high risk business where you don’t want to involve third party attestation where a lookalike digital signature can be poisoned or forged by malicious players to circulate a fake document, notice or announcement.
Evidences of the above claim:
- Comodo Breach: https://www.comodo.com/Comodo-Fraud-Incident-2011-03-23.html
- Mozilla Security Blog Post: https://blog.mozilla.org/security/2011/03/25/comodo-certificate-issue-follow-up/
- Electronic Frontier Foundation (EFF) DeepLinks Analysis: https://www.eff.org/deeplinks/2011/03/iranian-hackers-obtain-fraudulent-https
- DigiCert IP Addresses Flagged by Malware Report: https://knowledge.digicert.com/alerts/digicert-ip-addresses-flagged-by-malware-report
Using the Sovereign Certificates, the employees and associated partners can verify the certificates looking at the metadata in the certificate viewer (as explained in the screenshots above) or through the verification utility and ensure that the crucial document which contains business directives, policies, or decisions are coming from the authentic author or authority from the organisation whom the Sovereign Certificate belongs.
Scenario 2 – Digital Attestation of code and executables for close circle distribution
Imagine that you have a high security and sensitive code or executable which is for consmption within a closed circle of employees and partners. So, instead of attesting it through a third-party, your organisation wants to attest it internally with an organizational owner’s identity seal that’s mandatory to be verified before using the signed application or code.
This way when a malicious actor tries to supply a poisoned executable with a forged certificate it can be easily spotted because that executable will lack the authentic Sovereign Lineage Seal as it isn’t reproducable.
Scenario 3 – Locking of Approved Documents to counter tampering
In the corporate scenario, the drafts of business documents, computation sheets, proposals, notices, SOWs, etc. pass through multiple authors and at a point there are multiple versions which lose track of final approved draft to be locked.
It doesn’t make sense to use commercial DSC for such internal approvals and so these Sovereign Signature Certificates come handy as it’s not feasible to buy DSCs for every Manager who doesn’t need to sign and approve only internal documents and not external legal documents.
Counter Attack on IP Forgery and Asset Tampering
This multi-layered DELOL Sovereign Digital Signature Private CA Infrastructure enables organisation for establishing a safe and trusted digital environment which counters forgery and tampering of assets, documents and IPs through an Identity Locked Sovereign Linage Seal.
Block your Calendar
If your organisation deals with high sensitive assets and IP and want to explore this opportunity then feel free to schedule a call to witness the importance of this infrastructure in action.
Join Us As Authorized Distributors
This is a Channel Partnership Invitation for those MSMEs, Enterprises, Proprietary Firms and Individual Consultants as Authorized Distributors to resell our DELOL Shield Platform.